Azure AD
Configuration Steps
Setup Microsoft Entra ID / Azure AD as IdP (Identity Provider)
- Log in to Azure AD Portal.
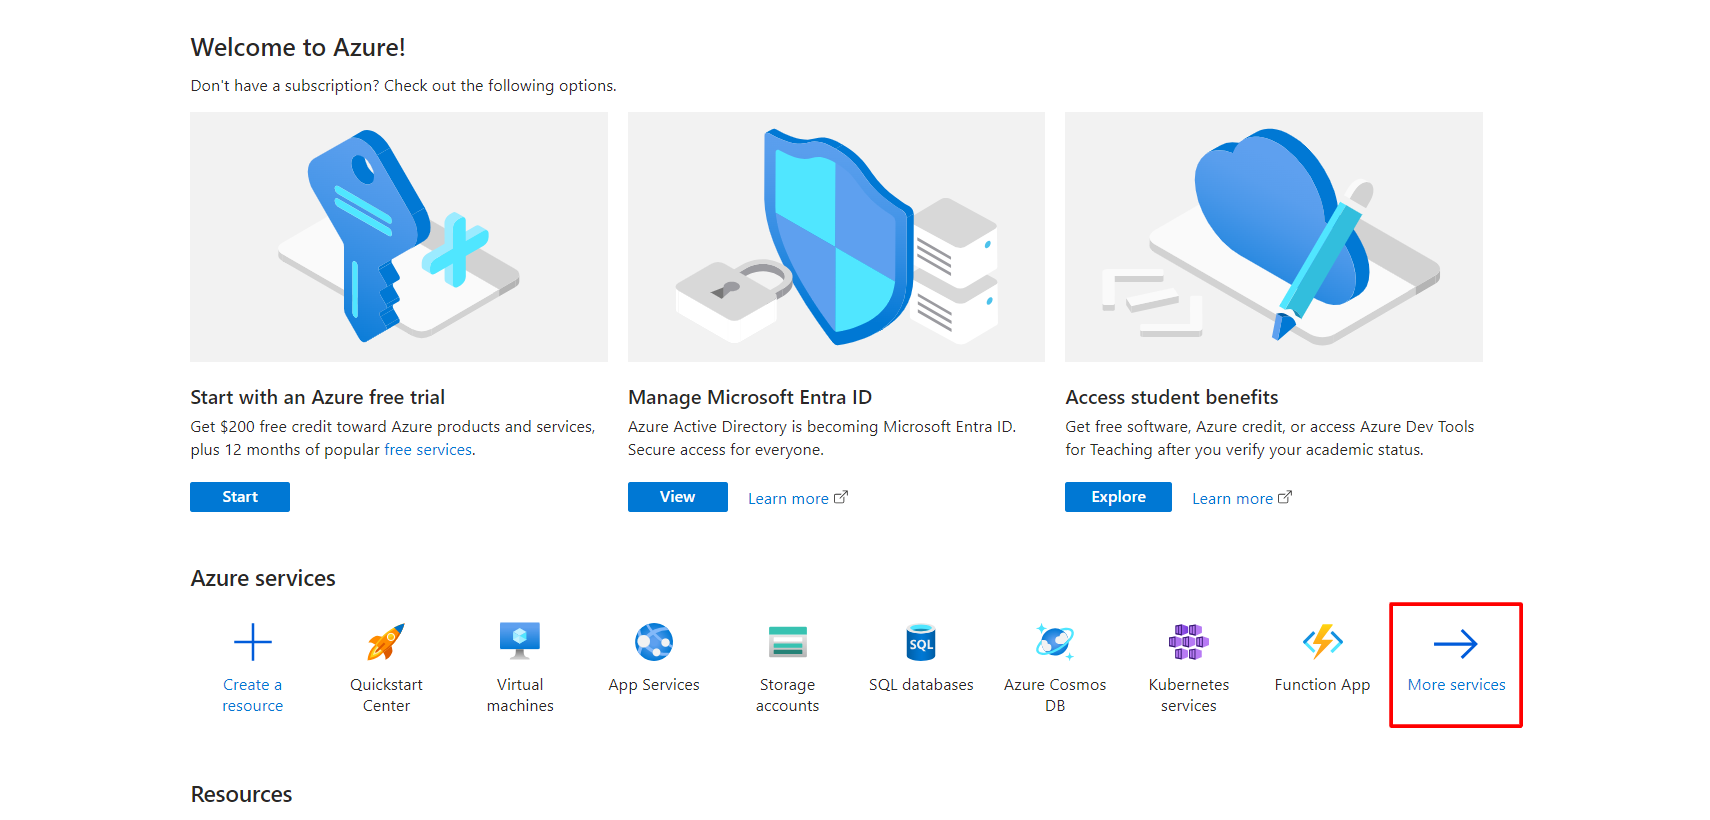
- Click on More services.
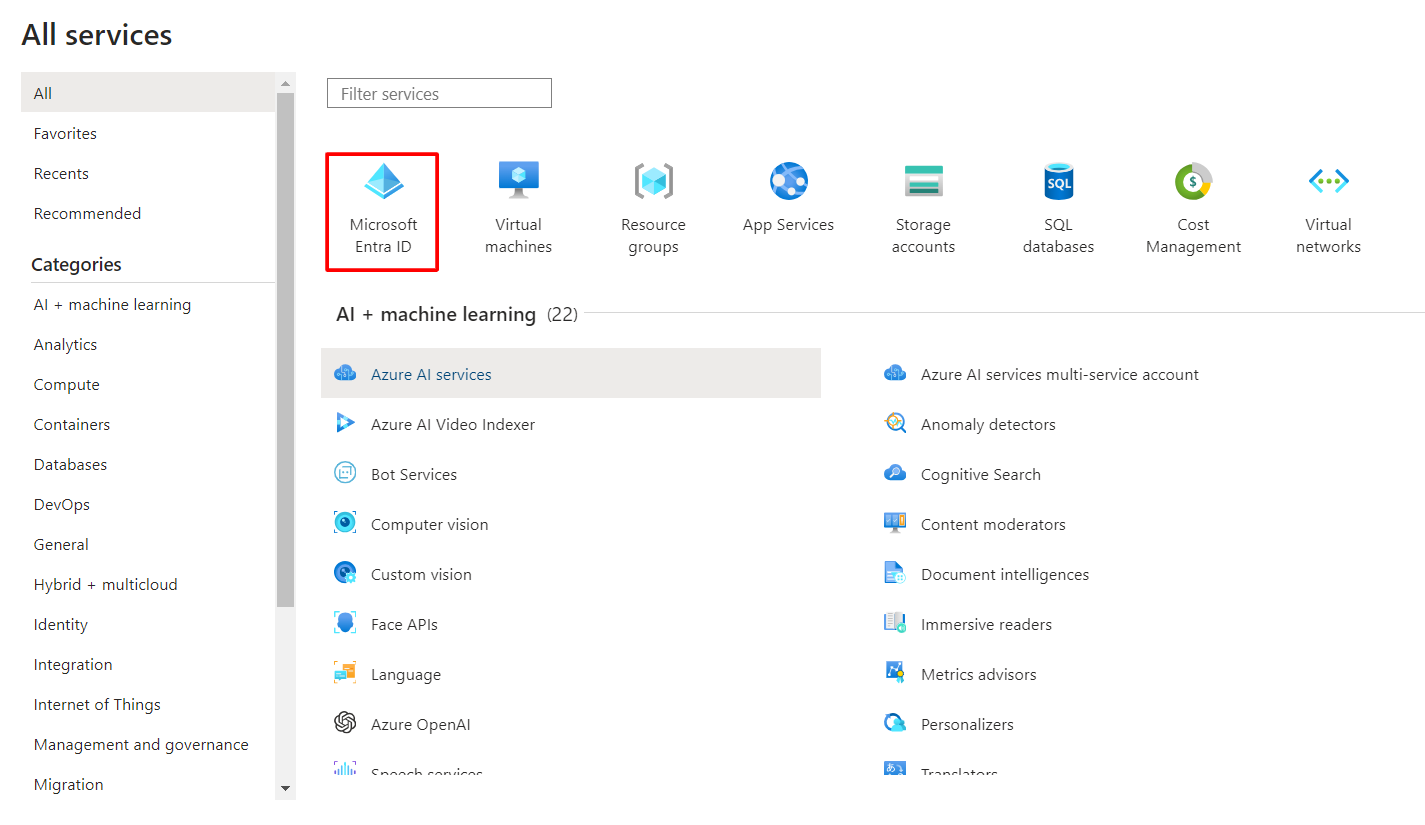
- Search and select Microsoft Entra ID.
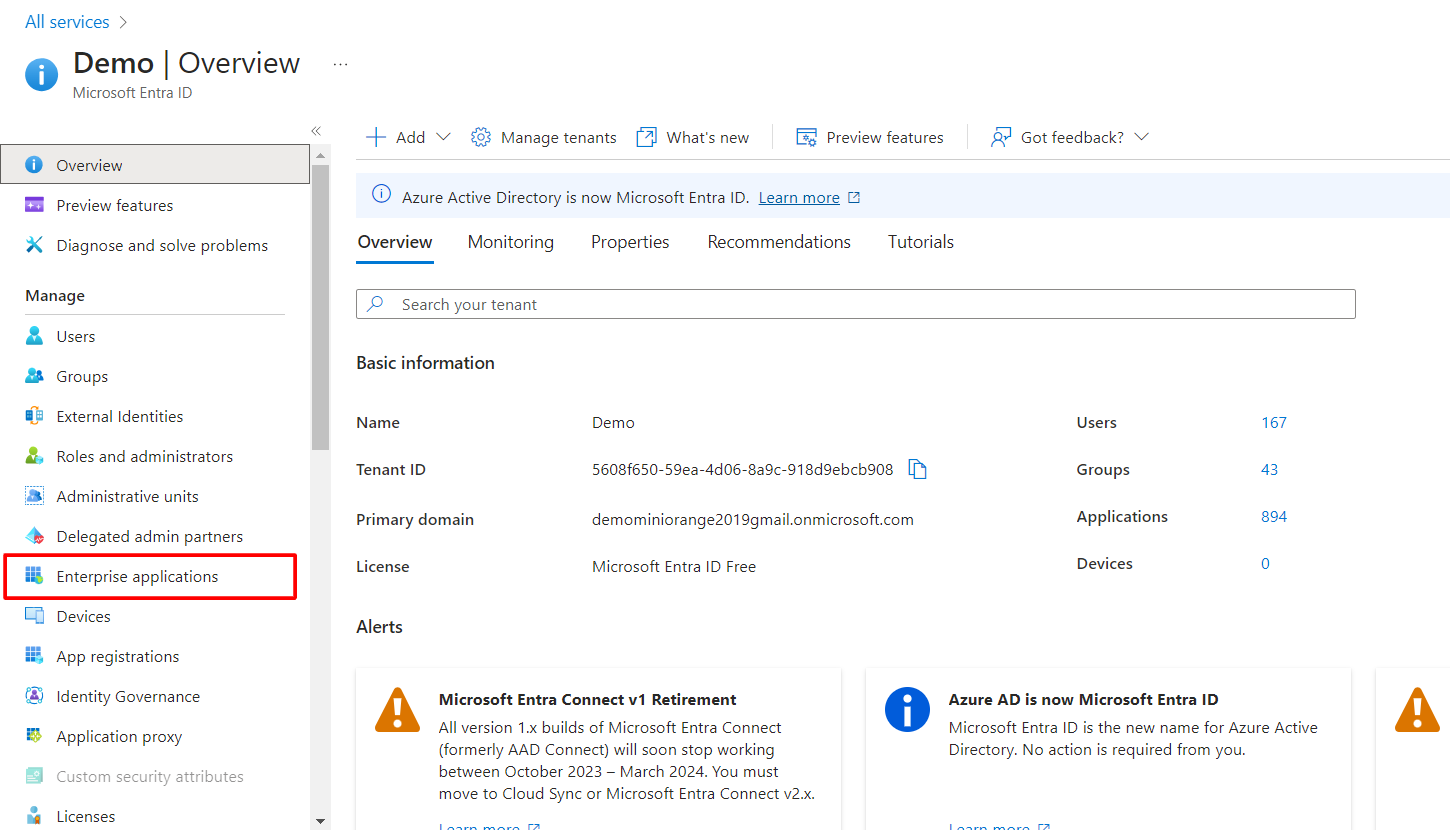
- Select Enterprise Application.
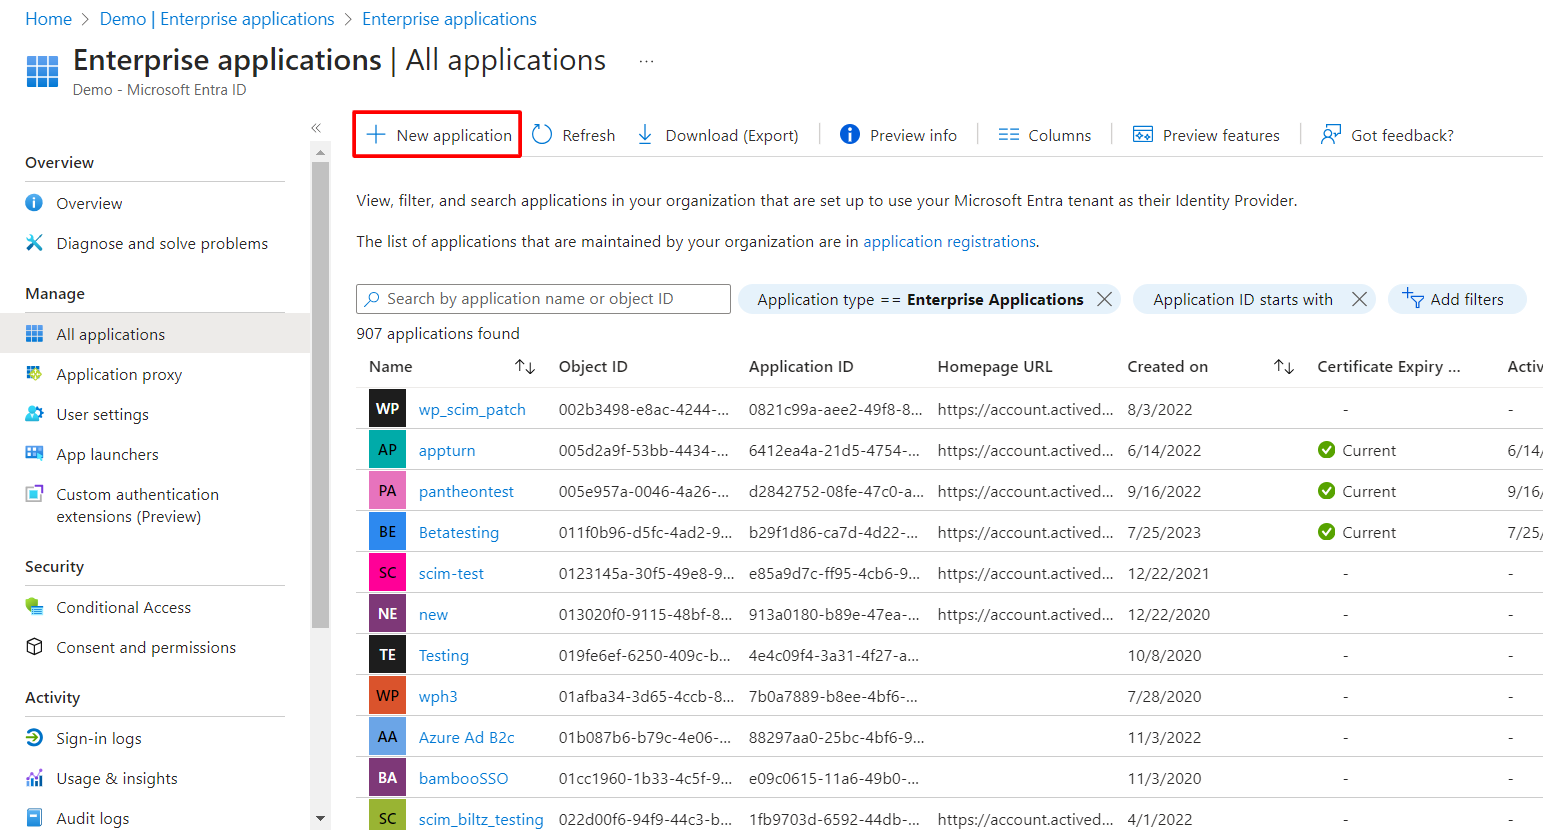
- Click on New Application.
- Click on Create your own Application.
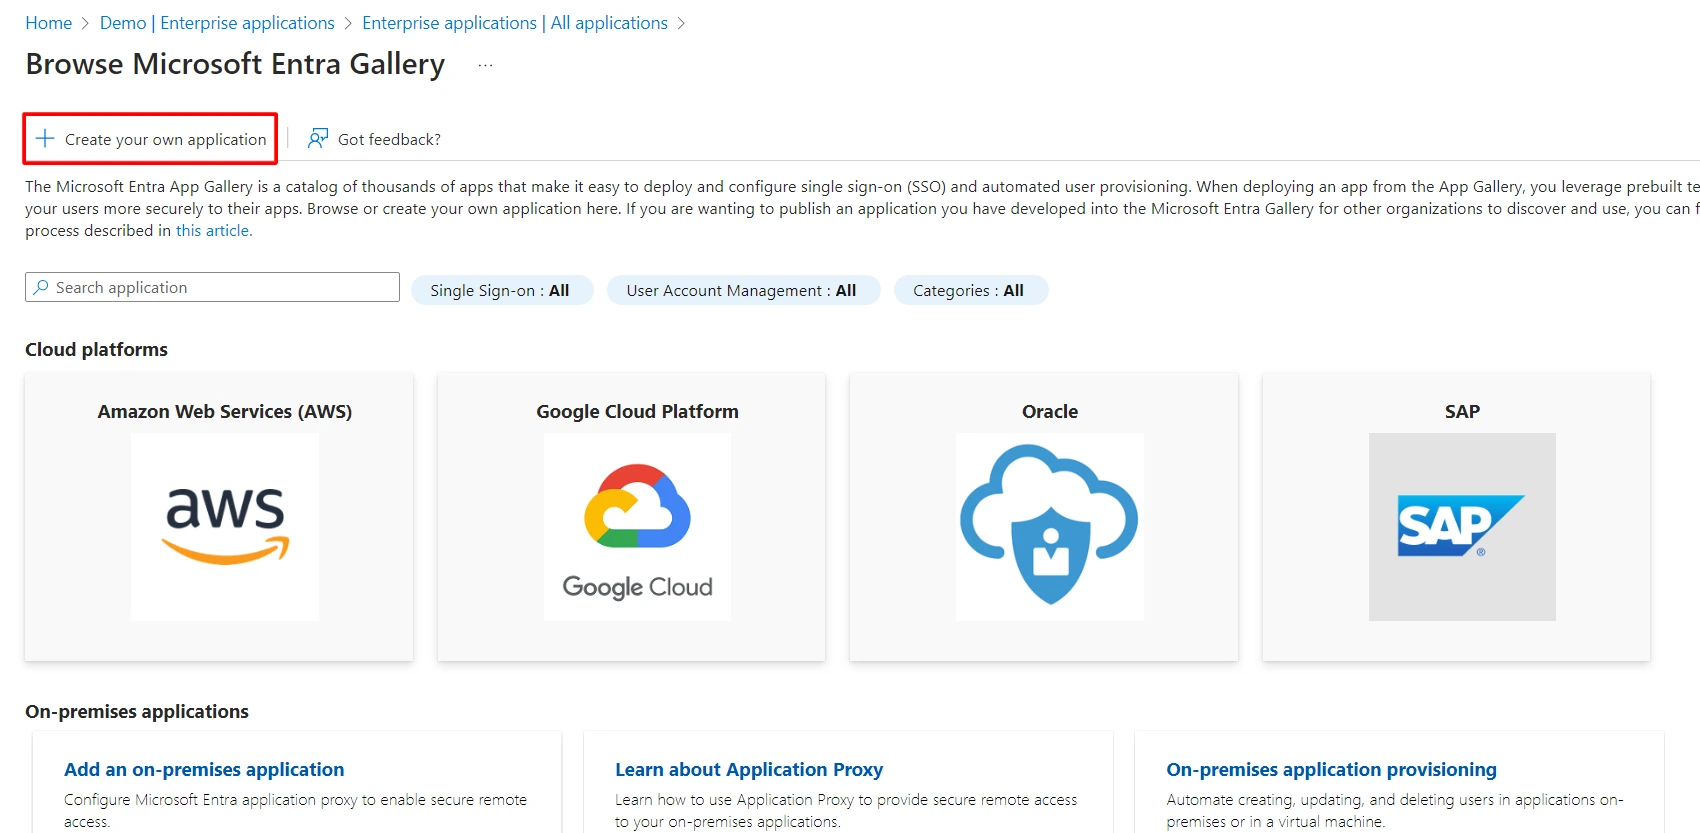
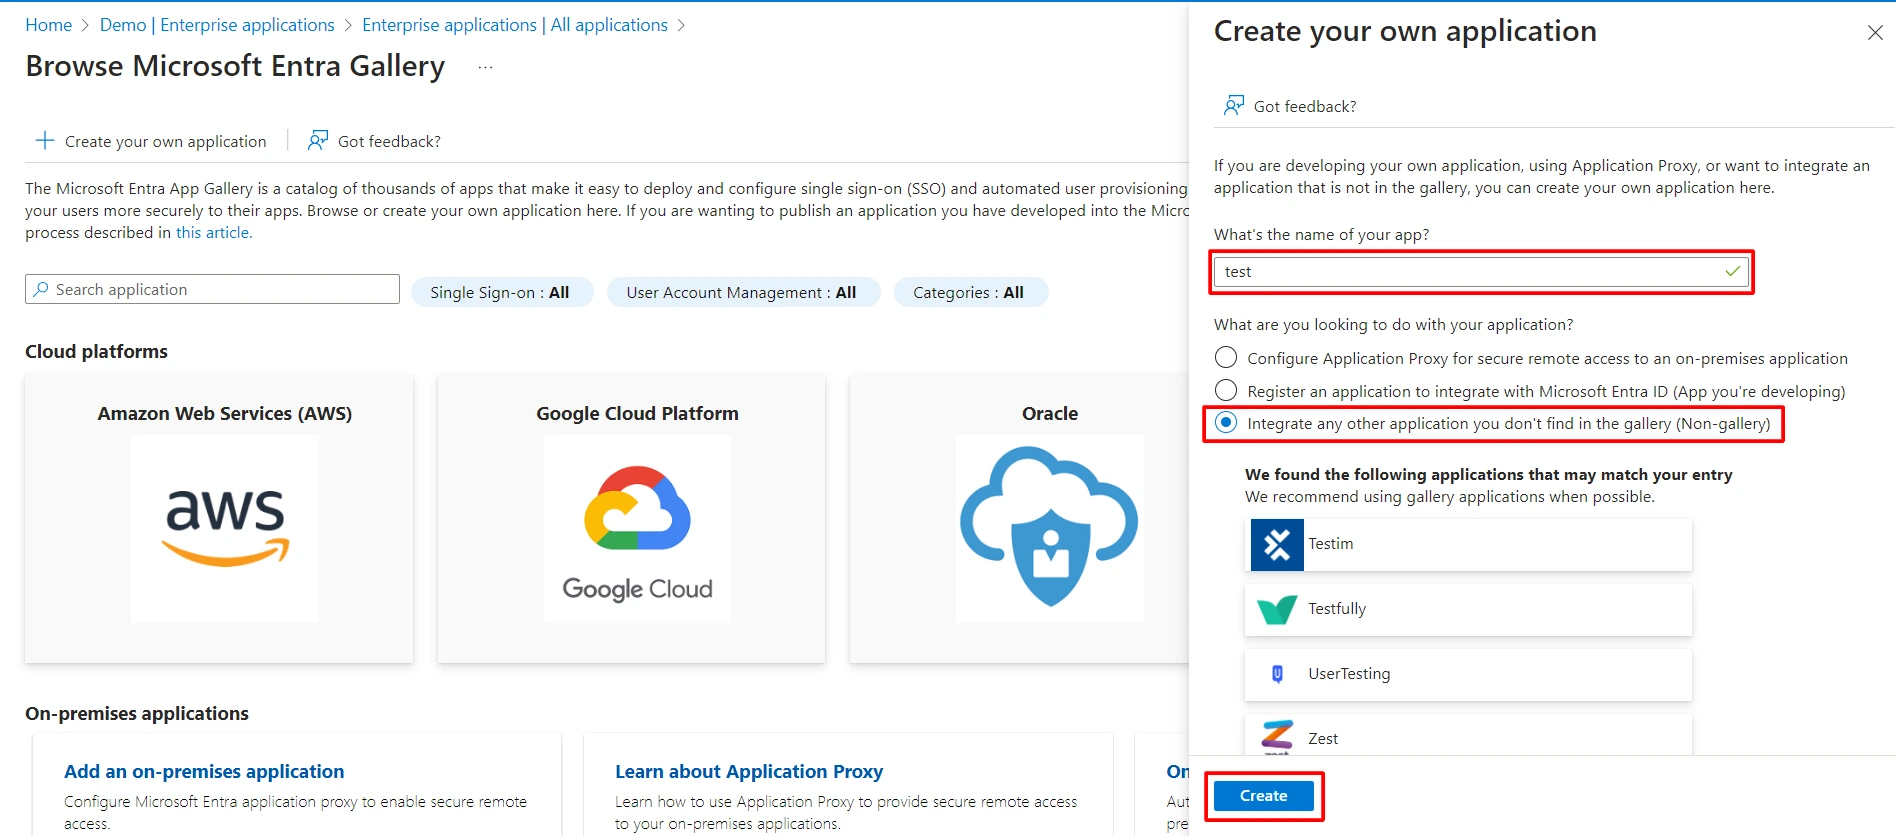
- Enter the name for your app, then select Non-gallery application section and click on Create button.
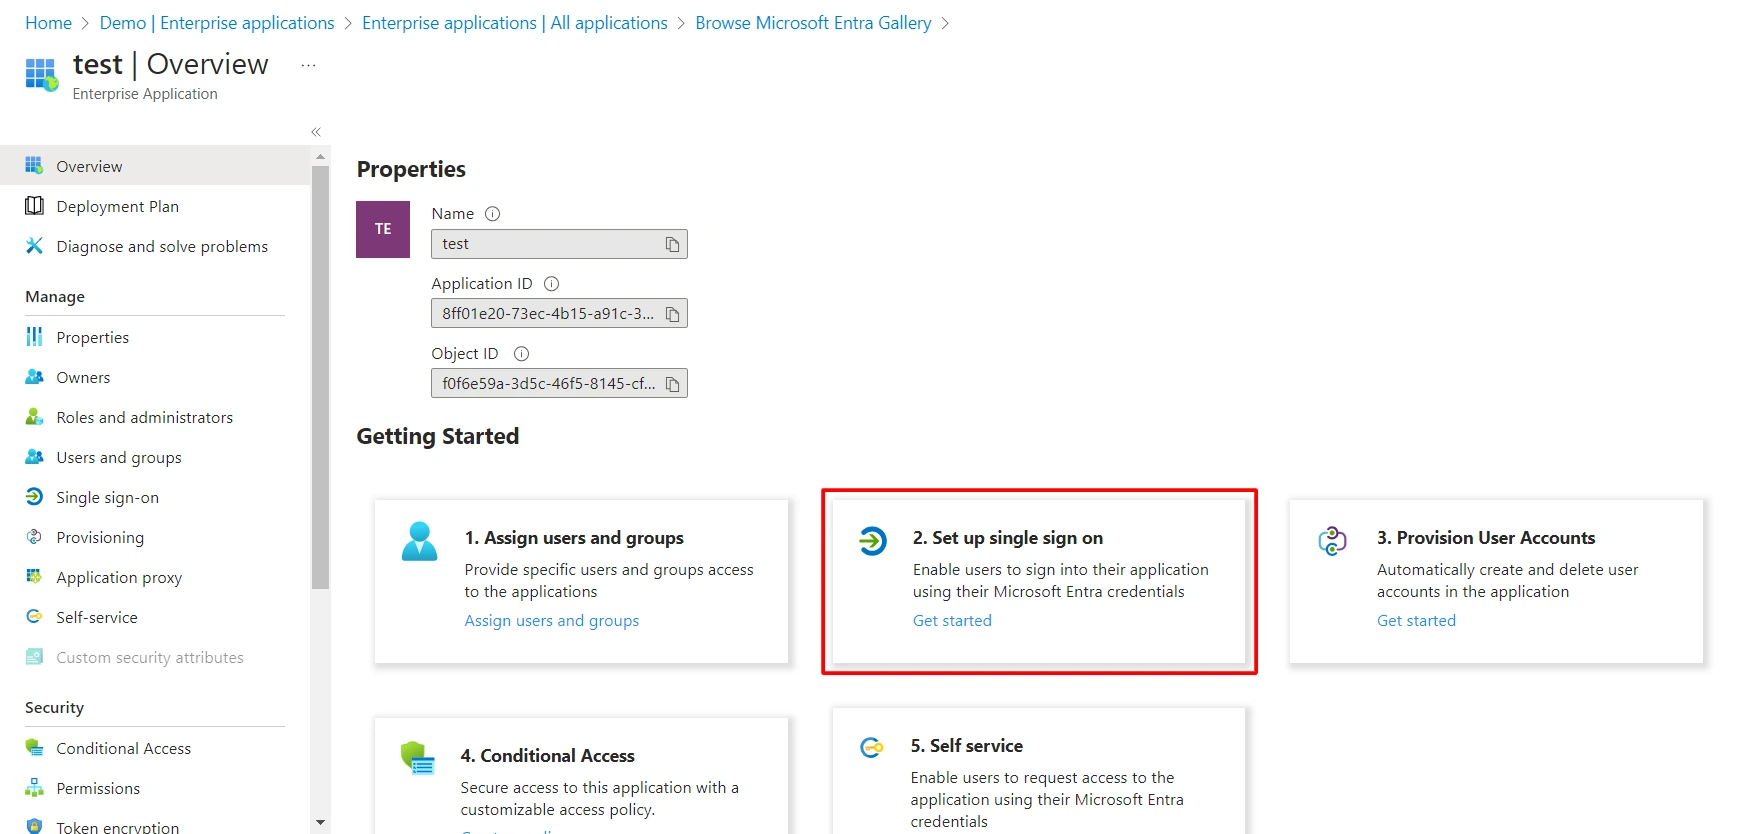
- Click on Set up single sign on.
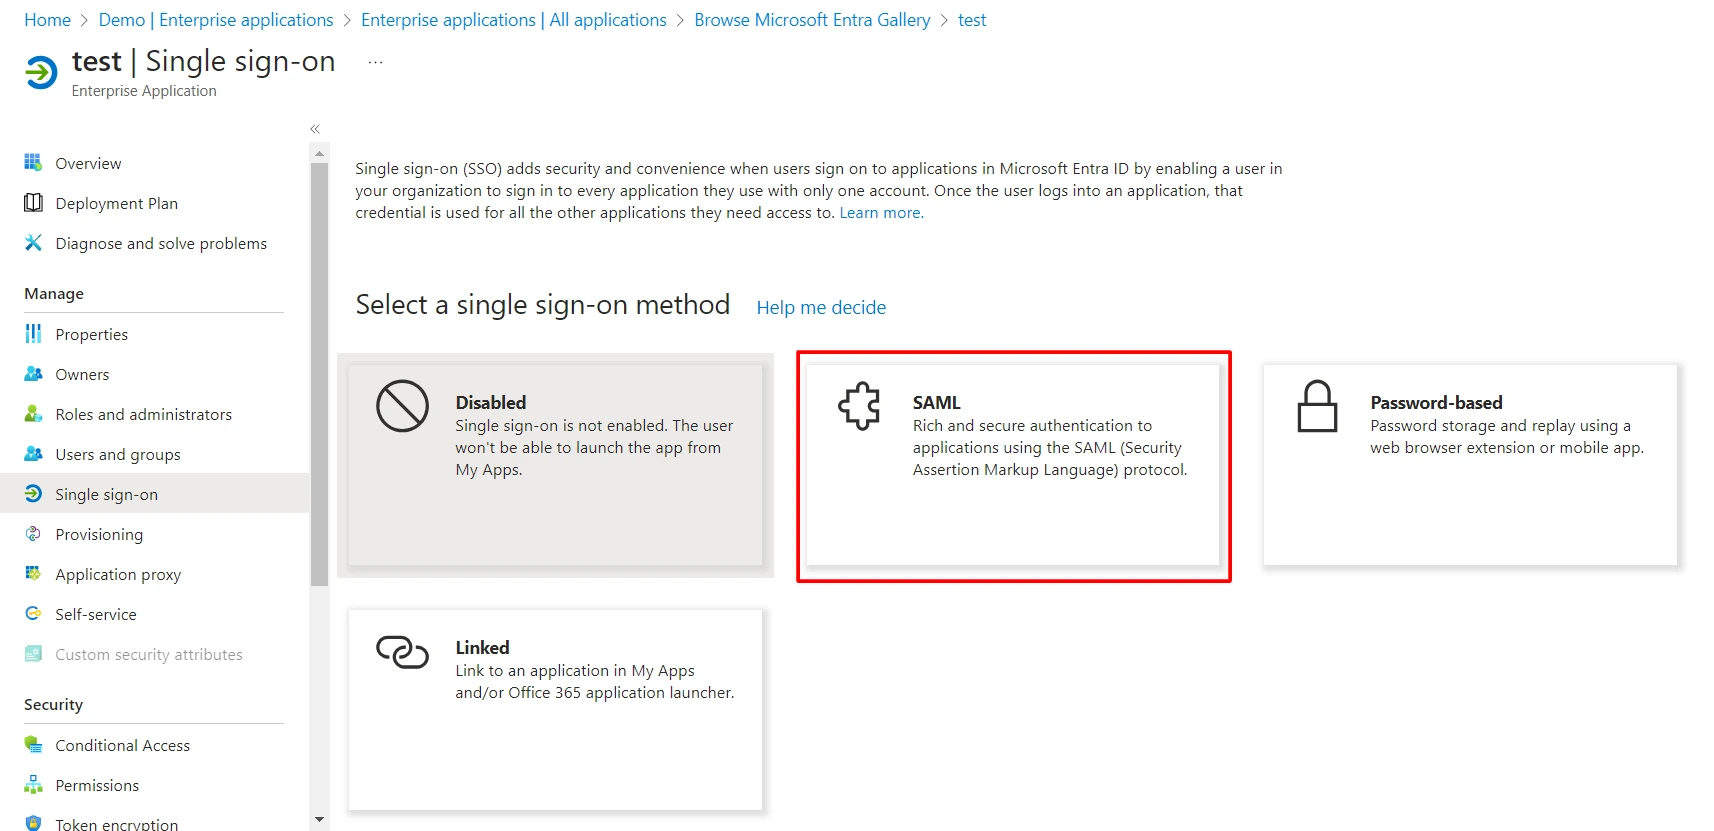
- Select the SAML tab.
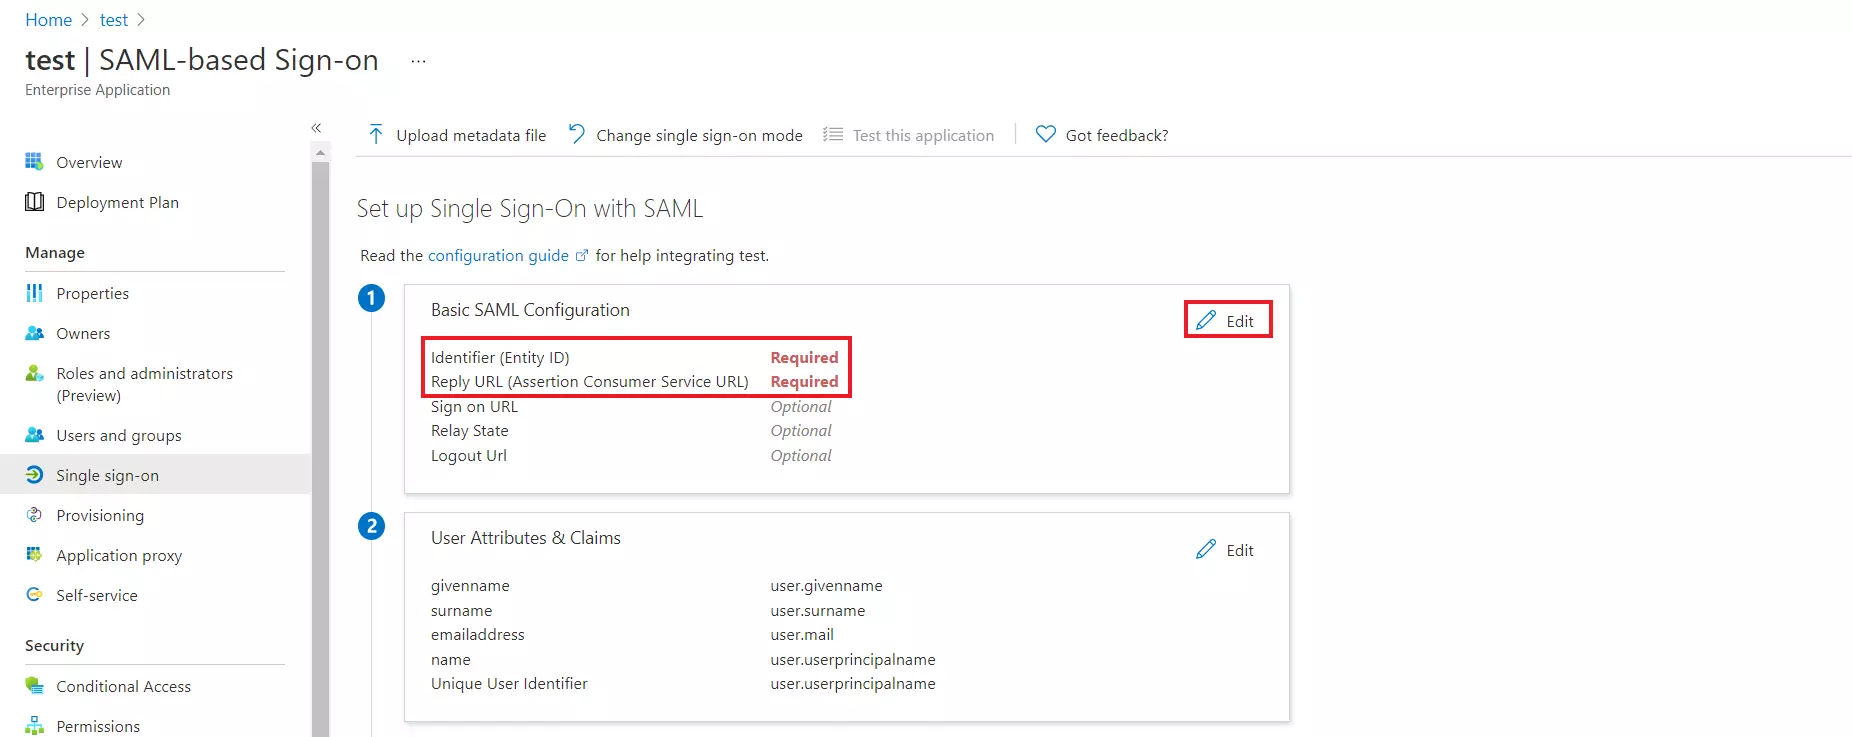
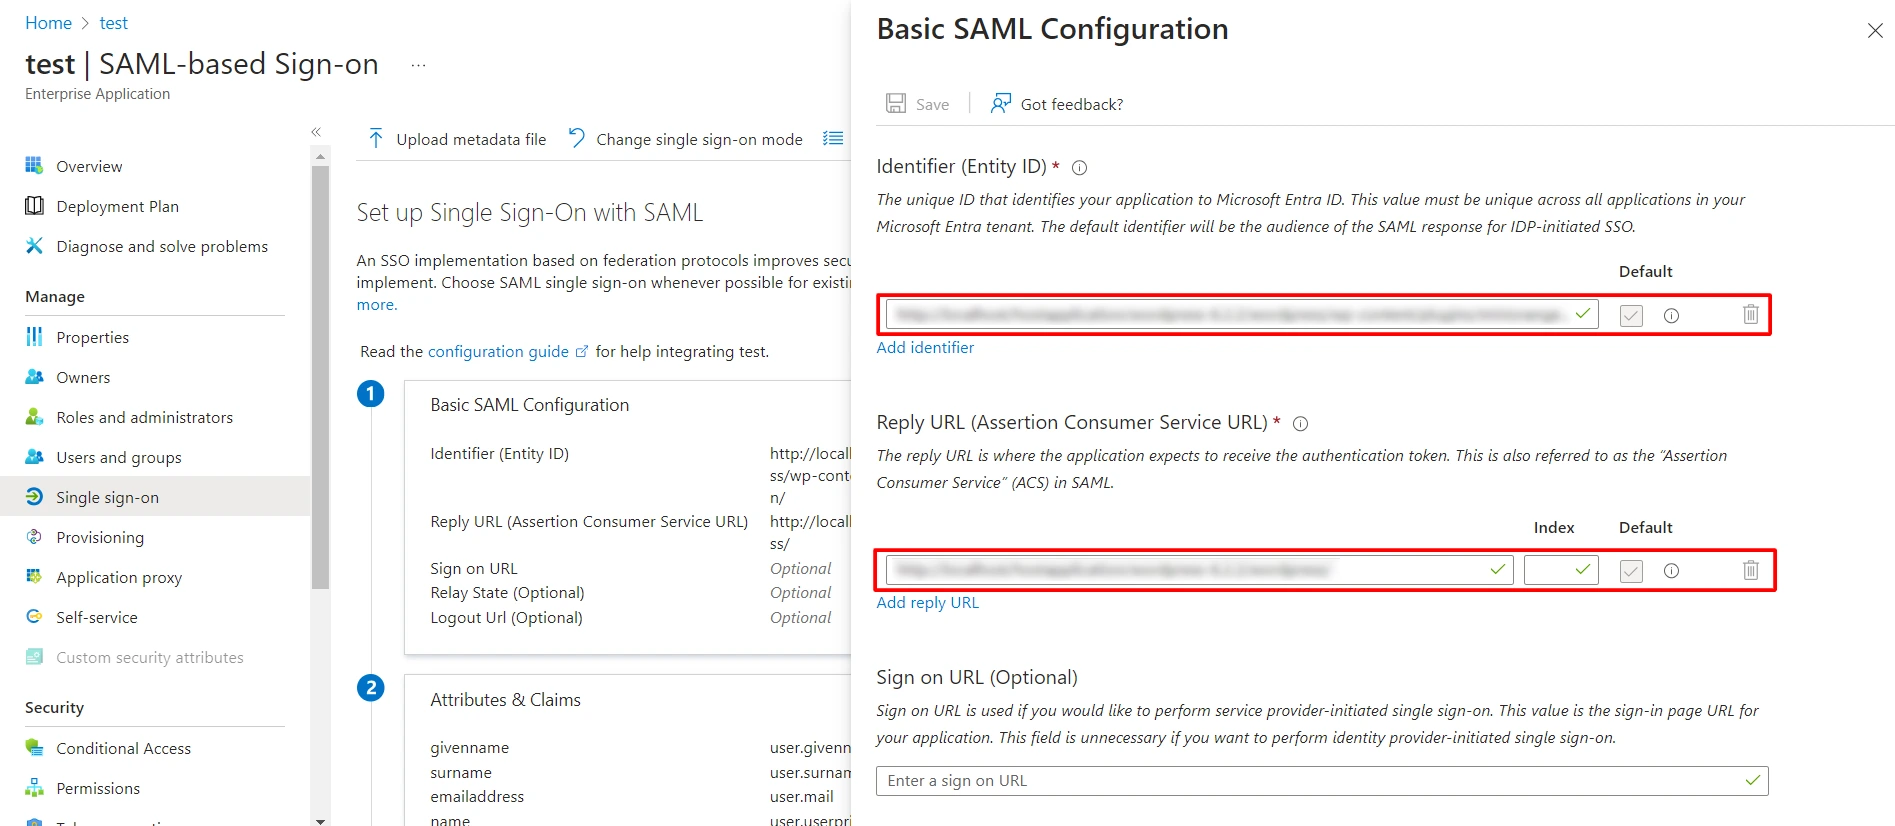
- After clicking on Edit, enter the Topaz SP Entity ID for Identifier and the ACS URL for Reply URL.
Note: For IDP-initiated SSO, the Sign On URL should be left blank.
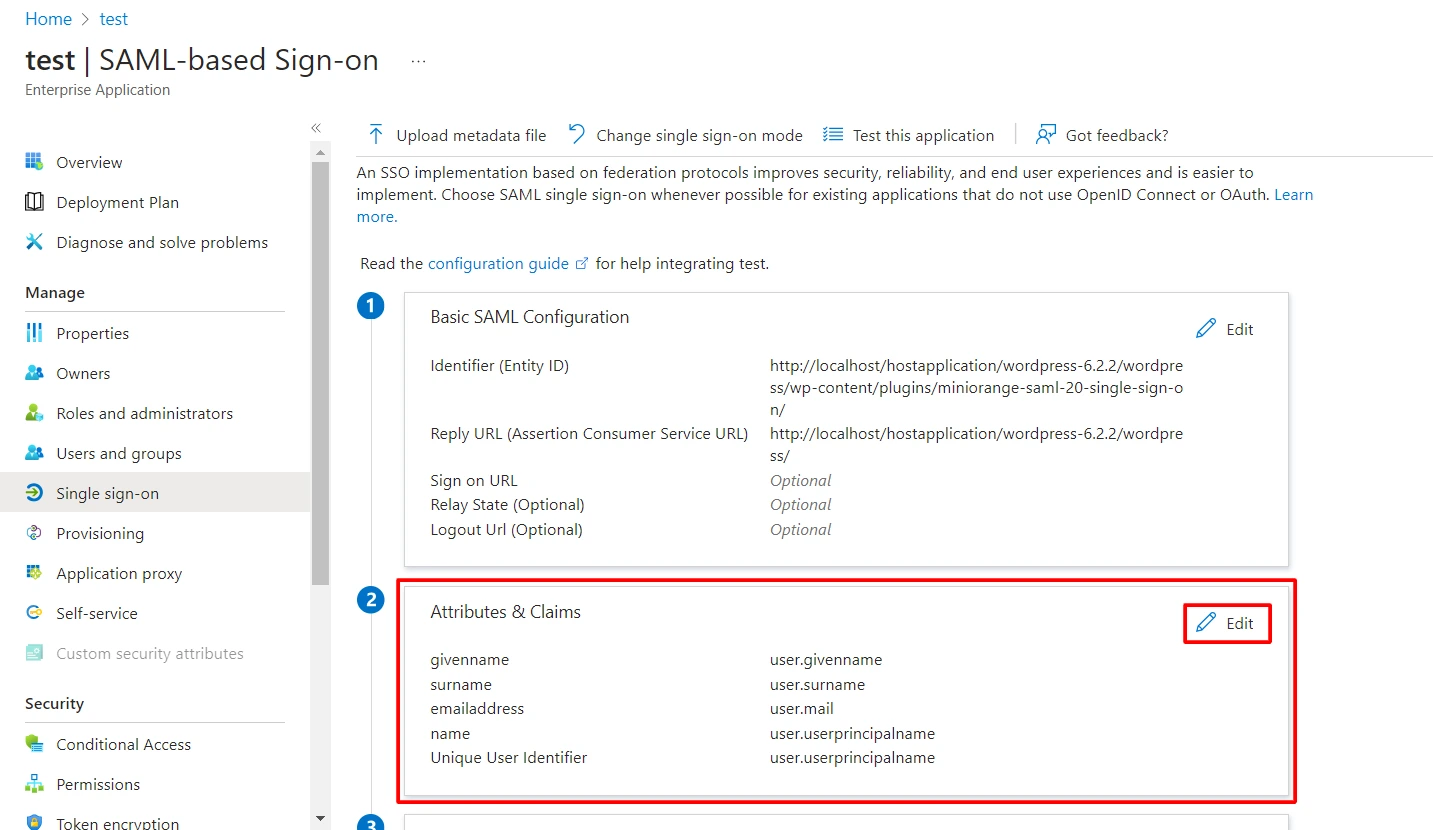
- By default, the following Attributes will be sent in the SAML response. You can view or edit the claims sent in the SAML response to the application under the Attributes tab.
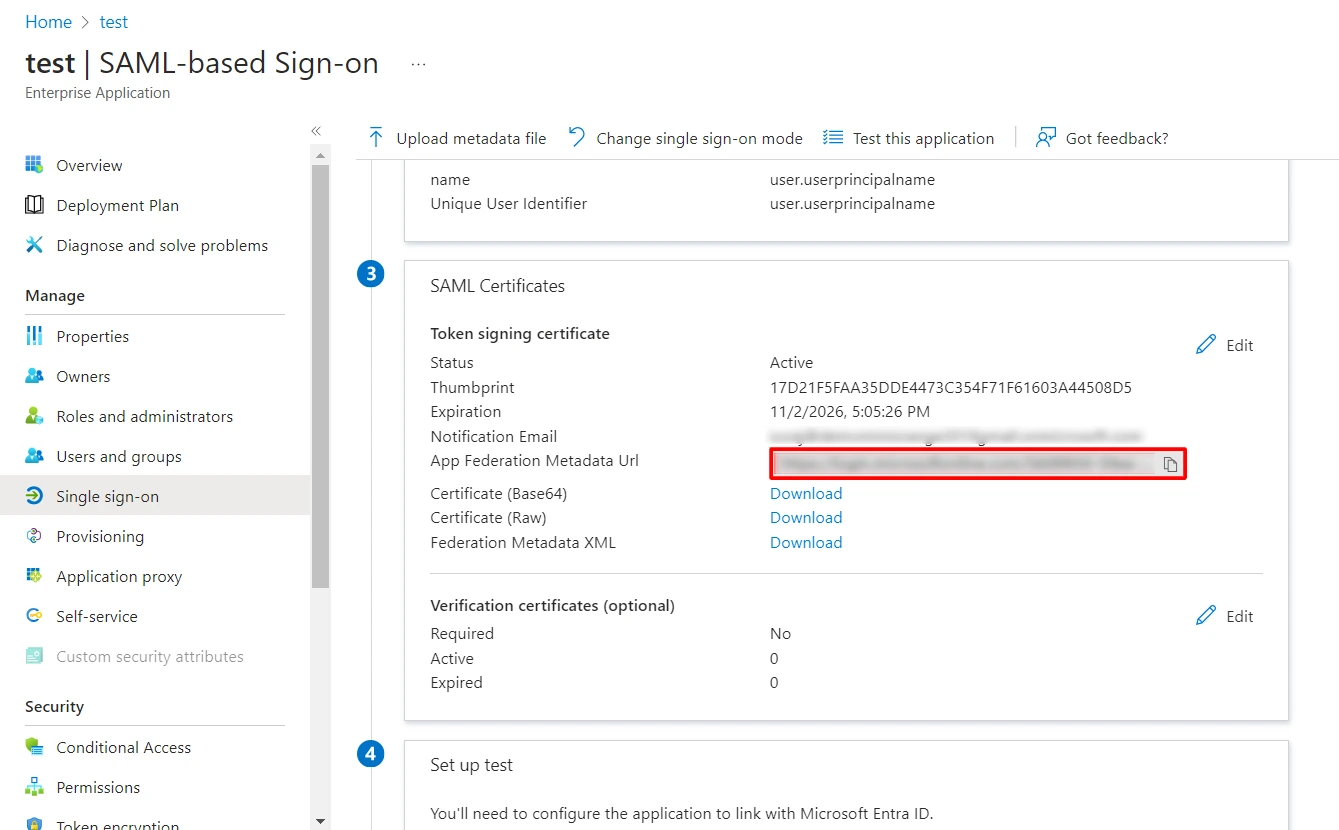
- Copy the App Federation Metadata URL (this is what you need to send to Topaz Labs)
Assign users and groups to your SAML application
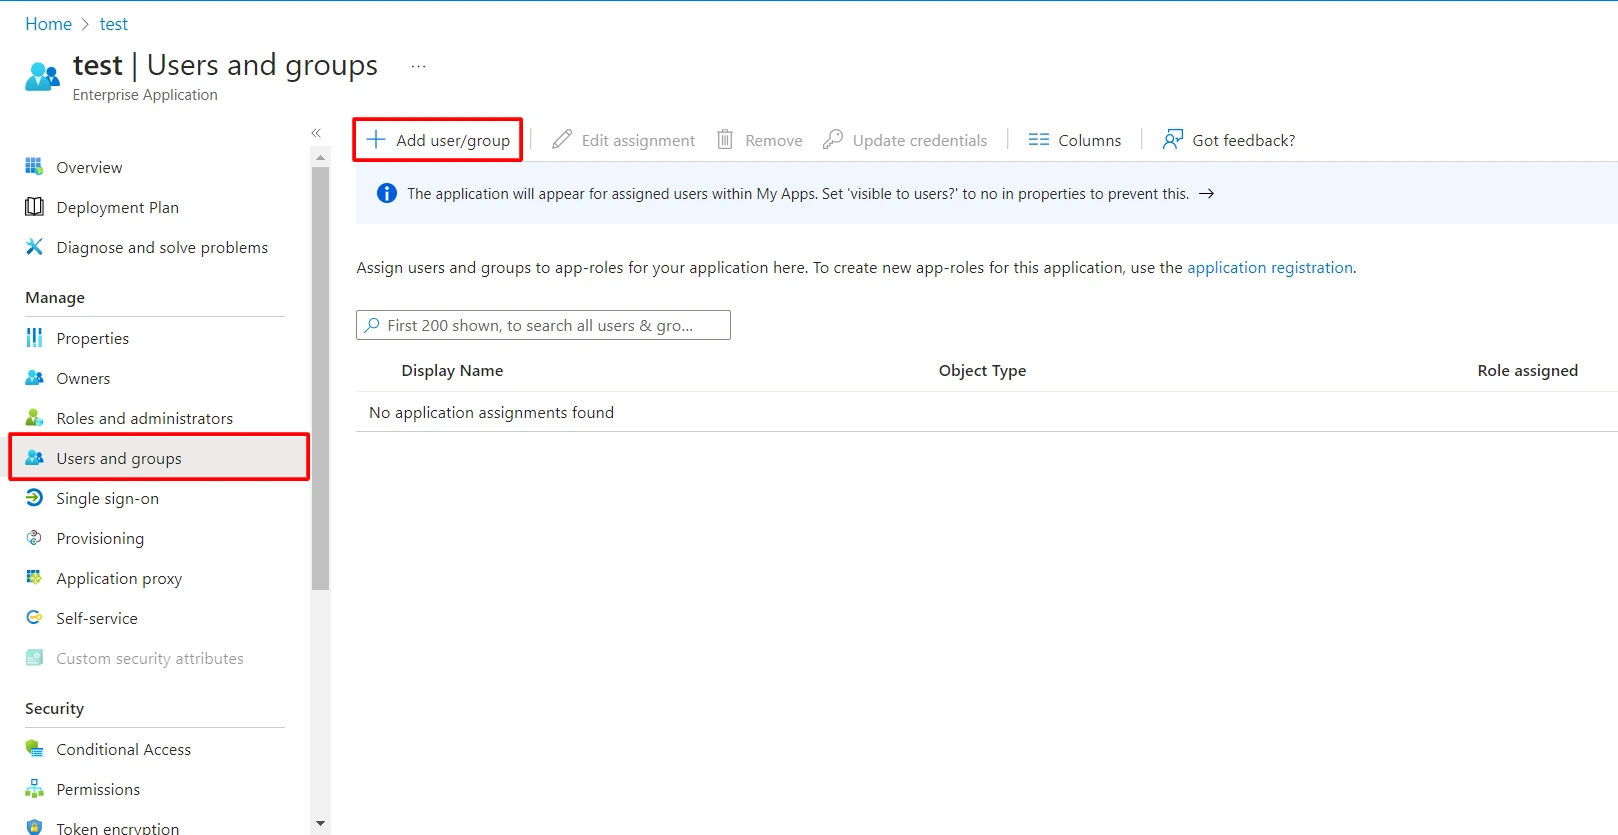
- Navigate to Users and groups tab and click on Add user/group.
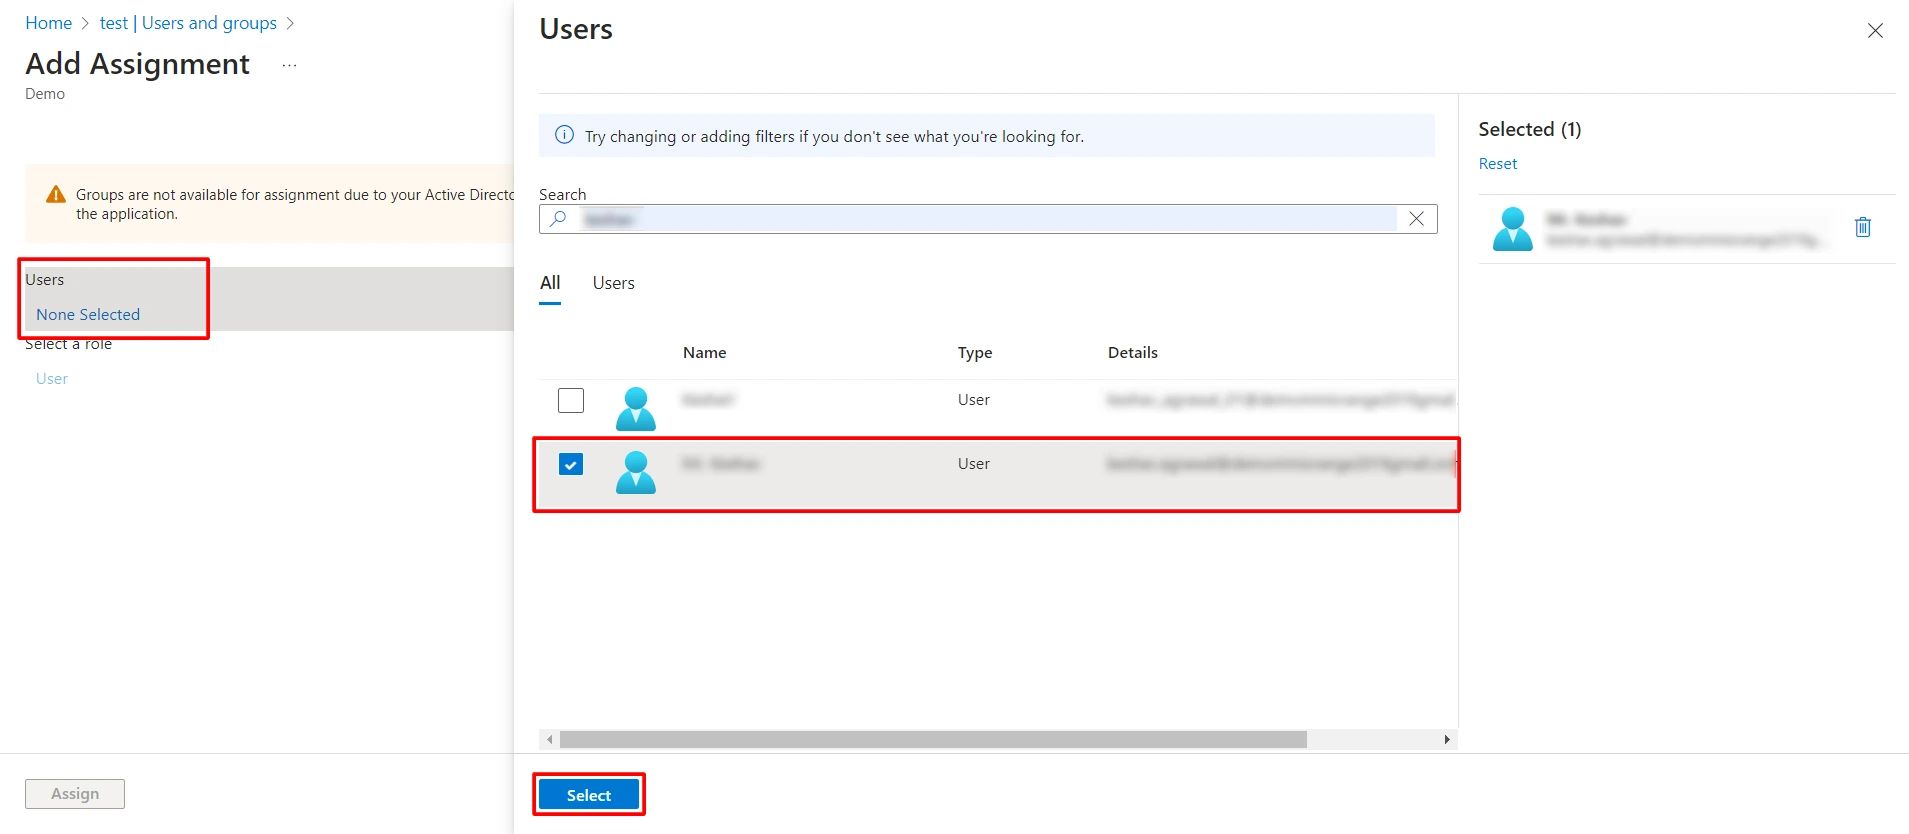
- Click on Users to assign the required user and then click on Select.
- After selecting users click on Assign button.
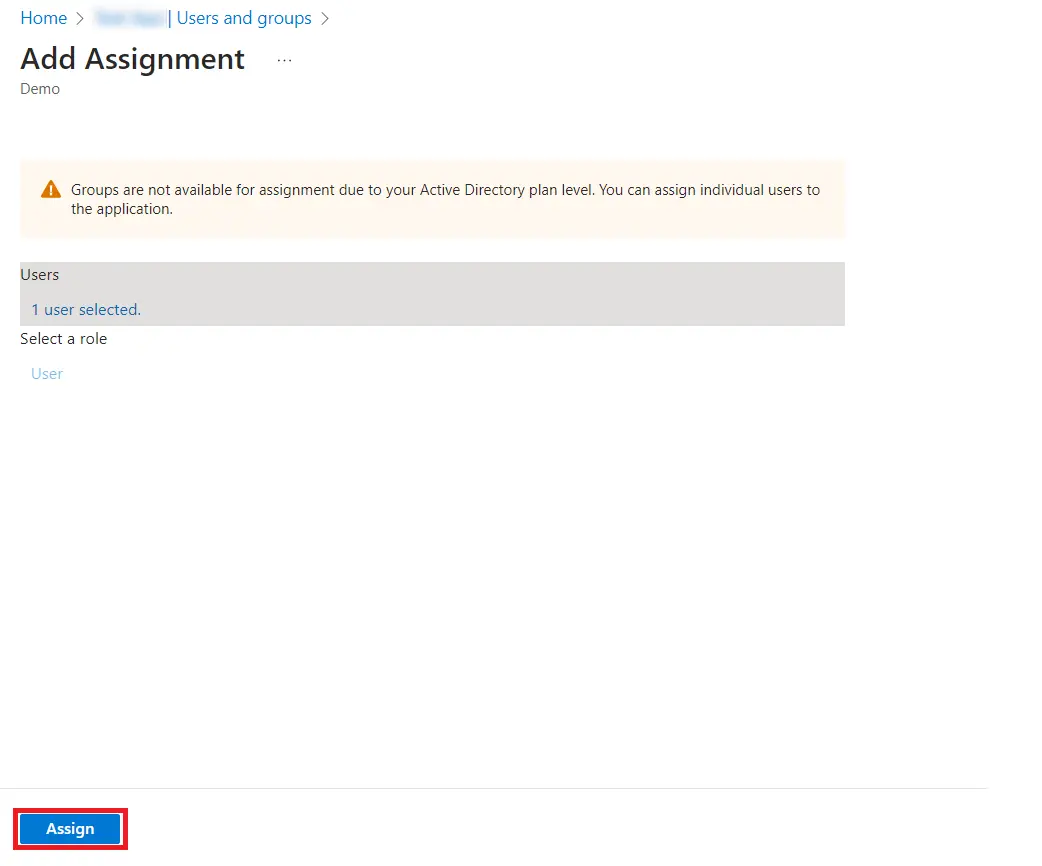
- You can also assign a role to your application under Select Role section.
- You have successfully configured Microsoft Entra ID / Azure AD as SAML IDP ( Identity Provider)